A client asks about yet another hosting option:
The VPS-2000HA-S includes the following resources:
6GB RAM (burstable)
150GB SSD Disk space
5TB Monthly Bandwidth
4 free dedicated IP's

A client asks about yet another hosting option:
The VPS-2000HA-S includes the following resources:
6GB RAM (burstable)
150GB SSD Disk space
5TB Monthly Bandwidth
4 free dedicated IP's

No, you should not. You should let us worry about them, and go back to your business.
Seriously, we're getting questions from all kinds of people about whether this matters. I'm a bit surprised that there is any question about that. Would you be concerned if your top salesperson was selling for somebody else? If your cashiers were jotting down credit card numbers when they charged a card? If your office became a well-known spot for illicit drug or gun dealers? If your office had a bunch of scammers squatting and running a pyramid scheme? If your confidential client information could be revealed as easily as using a bic pen on an old Kryptonite lock?
We've seen some variation of every single one of those scenarios. And all of them are possible with a remote code execution flaw in a web application, like yesterday's Drupal security vulnerability.
And yet people still

Drupal security updates generally come out on Wednesdays, to try to streamline everybody's time. WordPress security notices come out... well, whenever whichever feed you subscribe to bothers to announce something.

In September, Freelock was recognized as a leading web development company in Seattle by Clutch.


DevOps is the union of development, operations, and quality assurance -- but it's really the other way around.

Lots of stuff has been changing in Drupal 8 recently. In 8.3.0, a new experimental "layout discovery" module was added to core, which conflicted with the contrib "layout plugin" module.

As of today, the Drupal Matrix API module now supports sending messages to a room via Rules. Now you can automatically configure notifications to Matrix rooms without touching any code!

As I write, we're in the midst of a big Ransomware attack. Millions of computers have been infected, with their data encrypted, held ransom pending an extortion payment or deleted. Supposedly.

WordPress versus Drupal. Republican versus Democrat. Two debates where the differences seem so broad, people can't even seem to agree upon fundamental facts. Why? Why is it so hard to find an objective, clear comparison of WordPress and Drupal? I've had several people ask this.

When choosing any service provider, a crucial question is, "What happens if something goes wrong?" When you're choosing a hosting provider, we like to dig a bit deeper, and ask what risks are likely to be an issue for you?
Here are some of our questions:
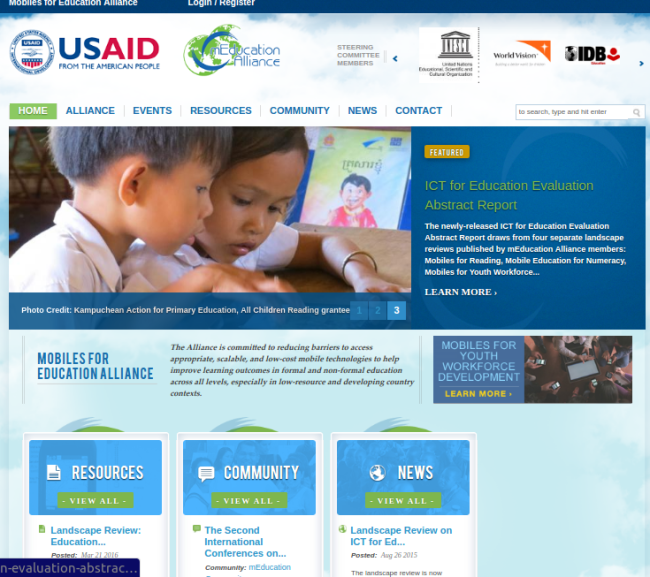
The product owners of the mEducation Alliance website contacted us in September, 2015 to provide ongoing monthly Drupal security and module updates. The site is a partnership between World Vision, USAID, Peace Corps, and UNICEF – just to name a few.


